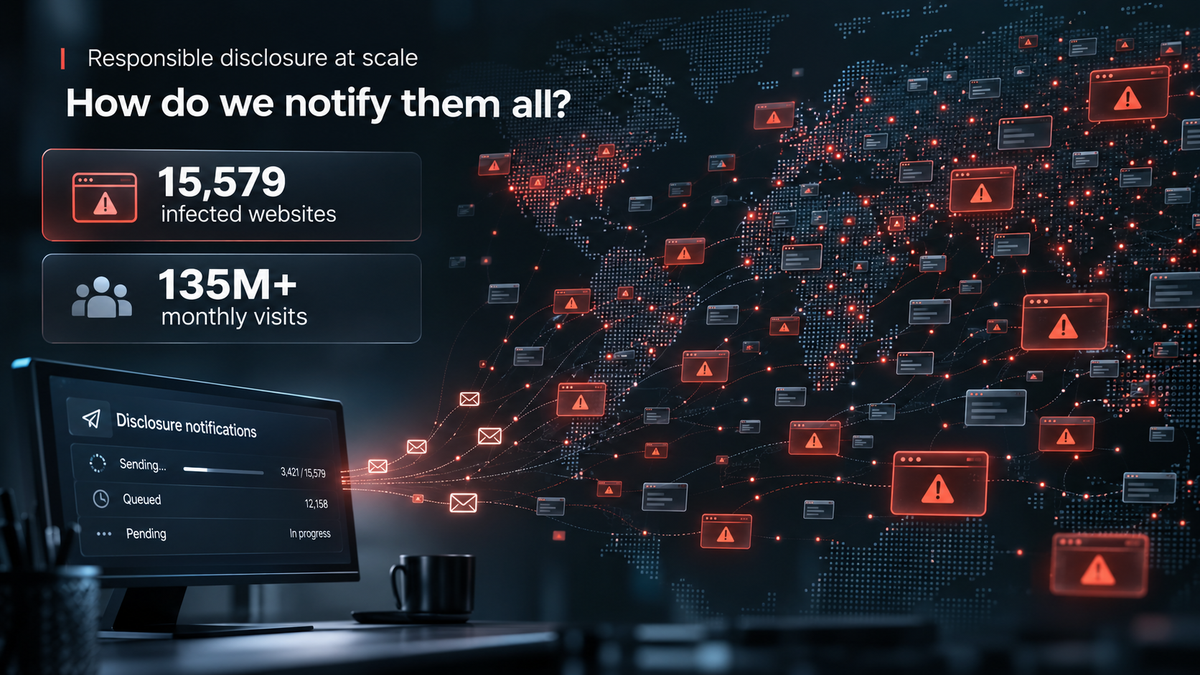
We've identified 15,579 websites that are currently infected with malicious JavaScript and between them, we conservatively estimate that they receive more than 135 million visits every month.
We know they're infected, and we have the evidence to back that up, but there's a problem: how on

Another option is looking for the
security.txt(toplevelor under.well-known/) of a site (that’s RFC 9116, which should have aContactfield with amailto:<contact address>field (althoughtel:<number>andhttps://<contact information page>are allowed, too, although far less common).Yeah, he mentioned
security.txtin the article, but complained that few implemented it.I guess that even if someone who apparently does computer security isn’t familiar with it, that Average Joe probably has no idea. Maybe there’s an argument that there should be some sort of Web browser support for “report problem with this page/site” that sends an email to an appropriate address with an URL for the page and comment so that people are more aware of it.
Now that you mention it… I decided to check our lemmy instances and both lemmy.today and feddit.org have a robots.txt (of course^^) but no security.txt *sigh*
Yours didn’t even bother to fill out the
/legalpage (which should also have contact information) although it’s a fixed part of the lemmy software with a link at the bottom of the site.